About
Table of Contents
Introduction#
Taha Marouani, a persistent, serious and ambitious Telecommunications Engineering student.
A self-learner who’s dedicating his time to focus on what really matters: Touching grass, making a change, and developing a solid career.
Armed with passion for Cybersecurity, Philosophy and Books, I’m finding my purpose through this non-sense by learning.
Academic Journey#
Engineering Degree in Telecommunications
2024-2027
With a strong focus on Signal Processing, Telecommunications, and Physics, I study the engineering principles behind how information is transmitted, processed, and received, contributing to the advancement of modern communication infrastructures.Operating SystemsLinuxCisco Packet TracerHuawei eNSPBashNetworkingCC++C#.NETNode.jsNext.jsReactNational Entrance Exams for Engineering School
2024-2027
As a PTSI student within the CPGE program, I underwent an intensive and rigorous scientific training focused on mathematics, physics, and engineering sciences. This was a very rewarding journey as it enhanced my analytical thinking, problem-solving abilities, and capacity to work under pressure (lots of pressure), all while building a solid foundation for advanced studies in engineering having the most important skills as an engineer.PhysicsMathsChemistryMachanicsElectronicsPythonProblem SolvingCritical ThinkingEngineeringWork under pressureBaccalaureat Degree with Honors
2020
Professional Experience#
Disclaimer
Due to hosting costs, I occasionally put down the AI-related projects. I am using any cloud provider’s free tier so I am saving costs to test and benchmark any current project.
If you need to see a project in action, you can ping me to host it for you in no time.
ODDO BHF Tunis - Vulnerability Management Intern
Summer 2025
- Engineered a multi-agents AI system for an internal Vulnerabilities Operations Center and Risk Management.
- Built a production-ready Agentic RAG system for internal operations.
- Built an AI-Augmented Kill Chain Detection system, to predict and remediate against advanced threats.
View the Codebase ↗
Ghrab VOC. RAGAIManagementAgentic AIAgentic RAGMulti-AgentAgentic SystemsBenchmarkingVulnerability ManagementFreelance - Security Consulting
Sep 2025 - Present
- Conducted white-box and black-box penetration tests of small business networks comprising 10–20 endpoints per VLAN.
- Assessed network segmentation, firewall rules and Wi-Fi security to identify unauthorized access paths and configuration weaknesses.
- Identified excessive privileges and access-control issues across cloud and on-premises environments, providing prioritized remediation guidance.
- Reviewed application deployments and CI/CD pipelines for exposed secrets, insecure permissions, misconfigurations and unsafe deployment practices.
RAGAIManagementAgentic AIAgentic RAGMulti-AgentAgentic SystemsBenchmarkingVulnerability ManagementBIAT IT - SOC & CTI Internship
Summer 2025
- Created an on-premise Open Source SOC Lab: Wazuh, TheHive, MISP, Cortex.
- Automated the deployment of different components using Docker containers.
- Reviewed and enhanced Threat Intelligence reports of previously filtered incidents.
- Studied and analyzed XDR/NDR logs to trace lateral movement attempts.
- Analyzed recent severe alerts and enhanced the final provided report.
- Performed a Threat Hunt based on traces from a critical recent incident.
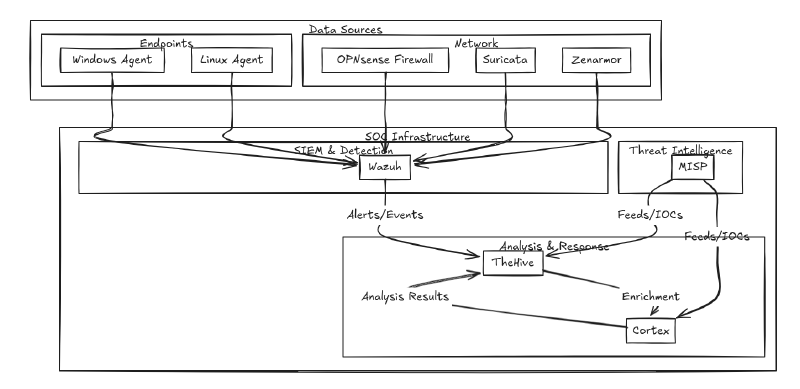
The Open Source on-premise, SOC Architecture I built. SOCFirewallWazuhIDSIPSThe HiveMISPCortexSIEMSOARActive DirectoryWindowsThreat HuntingThreat IntelligenceSecurity OperationsLog AnalysisCTF Author & Infrastructure Maintainer
March 2025 - Now
- Co-founded Securinets ENIT, the local branch of the Tunisian national cybersecurity organization.
- Maintained and orchestrated 2 national CTFs and 2 local CTFs serving over 200 teams with 0 downtime.
- Authored 15+ DFIR, Reverse Engineering and Pwn tasks.
- Optimized CI/CD and GitHub workflows for the repositories of the CTFs to manage collaboration between the authors.
Cat The Flag 2.0: Second edition of Securinets ENIT National CTF CTFOrchestrationInfrastructureCloud (GCP/AWS)High AvailabilityReverse EngineeringBinary ExploitationDFIRPwnGitHubCI/CDAutomationDevOps WorkflowsTeam CollaborationScalability
Projects#
Advanced OPSEC-compliant and Resilient C2 Infrastructure for Red Team Operations
current project
- Engineered a resilient, fault-friendly and reliable C2 architecture for long and short red team engagements.
- Used and managed resources from multiple cloud providers (AWS, GCP, Digital Ocean and Cloudflare) to craft a multi-cloud infrastruccture.
- Used domain fronting for new network-level blending in and evasion.
- Designed well hardened redirectors to not leak informations about our stack in-use.
- Setup Mythic C2 with HTTP, HTTPx and DNS malleable profiles for interacting with the implant.
- Designed fail-over domains going through multiple cloud providers' instances to avoid single points of failure.
- Designed an advanced phishing infrastructure made for fully undetected Initial Access.
- And much more
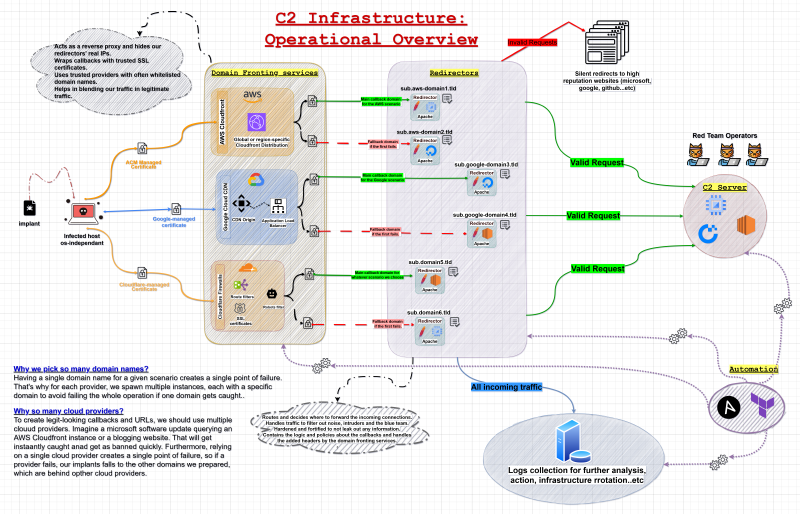
Advanced C2 Infrastructure. IAMMulti-CloudInfrastructure as CodeAnsibleTerraformDomain FrontingTraffic BlendingOpSec & HardeningMythic C2 FrameworkMalleable C2 ProfilesReverse Proxy (Apache)Initial AccessPost-ExploitationLong-HaulShort-HaulPersistenceEvasionAutomated FailoverConfidential RF Threat Detection Platform - Public-Sector Engagement
November - April 2025
- Created an on-premise and cloud Malware Analysis Lab.
- Analyzed Zeus Trojan - Banking Version and WannaCry Ransomware.
- Performed Static and Dynamic analysis on different samples.
- Reverse Engineered multiple samples and classified differences in tradecraft.
- Replicated malware behavior and re-created their base source codes.
- Researched coverd evasion techniques and tactics and mapped them to MITRE IDs.
Everything That Transmits Malware AnalysisReverse EngineeringBinary AnalysisStatic AnalysisDynamic AnalysisAssembly (x86)Windows PEAnti-Debugging & EvasionC2 CommunicationWiresharkProcMonIDA / GhidraMITRE ATT&CK MappingTrojanRansomwareEvasive, OPSEC-Compliant Phishing Infrastructure for MFA Bypass
current project
- Engineered a Multi-Layered APT-style phishing infrastructure.
- Used trusted cloud services to achieve seamless evasion.
- Crafted multiple Evilginx phishlets for multiple trusted services and websites.
Advanced C2 Infrastructure. IAMMulti-CloudInfrastructure as CodeAnsibleTerraformDomain FrontingTraffic BlendingOpSec & HardeningMythic C2 FrameworkMalleable C2 ProfilesReverse Proxy (Apache)Initial AccessPost-ExploitationLong-HaulShort-HaulPersistenceEvasionAutomated FailoverMalware Analysis Project
November - April 2025
- Created an on-premise and cloud Malware Analysis Lab.
- Analyzed Zeus Trojan - Banking Version and WannaCry Ransomware.
- Performed Static and Dynamic analysis on different samples.
- Reverse Engineered multiple samples and classified differences in tradecraft.
- Replicated malware behavior and re-created their base source codes.
- Researched coverd evasion techniques and tactics and mapped them to MITRE IDs.
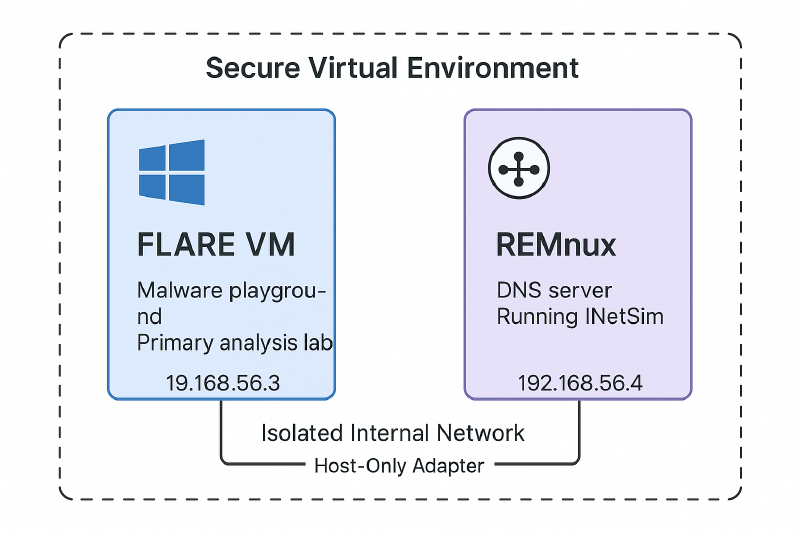
Malware Analysis Lab Architecture. Malware AnalysisReverse EngineeringBinary AnalysisStatic AnalysisDynamic AnalysisAssembly (x86)Windows PEAnti-Debugging & EvasionC2 CommunicationWiresharkProcMonIDA / GhidraMITRE ATT&CK MappingTrojanRansomware
CTFs and Ranking#
HackTheBox Profile#
Since Summer 2025, I started seriously and methodologically attacking HackTheBox Labs and sherlocks.
You can find my profile stats down below.

CTFTime Profile#
I’m a part of Curiosity, a Tunisian CTF Team formed in July 2025.
So far, we achieved high rankings in major international and national CTFs,
I currently focus on:
- DFIR
- Reverse Engineering
- and some Binary Exploitation tasks.
You can view my CTFTime Profile Here .
There are no articles to list here yet.